ISO 27001 certification in Uganda for organisations
ISO 27001 certification in Uganda is how banks, universities, hospitals, public agencies, NGOs and technology firms show that information security is a managed system rather than a pile of tools. NAM QMS trains the team that will run that system, offers a free gap analysis, and prepares the organisation for an independent audit. We are not the body that issues the certificate.
Train the team that owns the ISMS
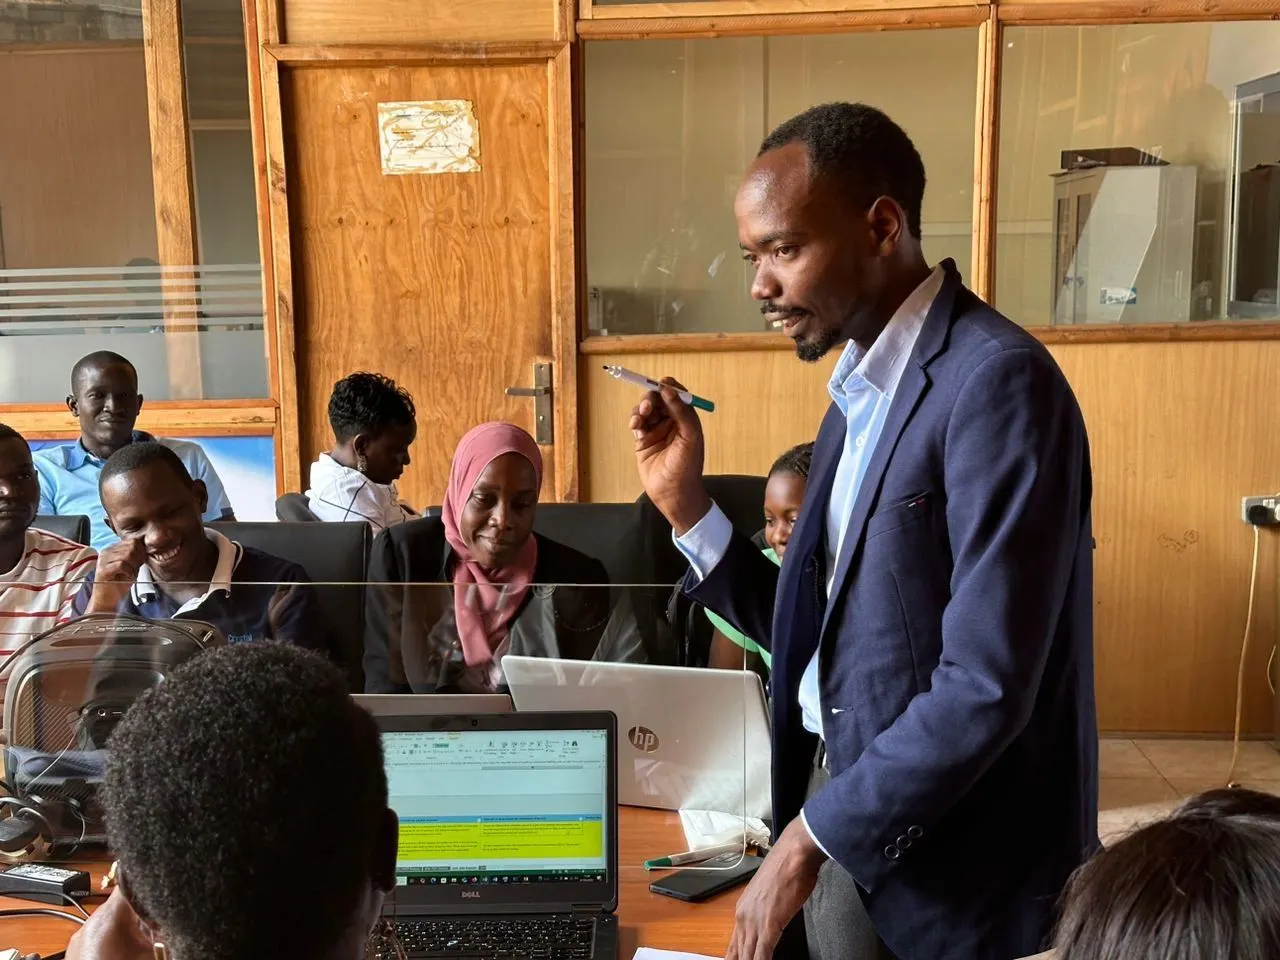
An information security management system fails when only the IT supplier understands it. We train the organisation's own people: the staff who classify information, approve access, manage suppliers, respond to incidents and audit the controls. In-house delivery uses your processes and your sites. The company format is set out on the internal audit training page.
For staff who need the full Lead Auditor programme, use the published ISO 27001:2022 Lead Auditor course page. The fee for an individual seat and for a team is on that course page. Send the people who will audit your ISMS. Passing a course is not ISO 27001 certification of the organisation.
A free gap analysis of scope, risk and controls
The free ISO gap analysis starts with scope. Which information, which systems, which sites and which suppliers are inside the ISMS, and which are honestly outside it? We then look at whether risks are assessed, whether a treatment plan exists, and whether the controls you claim are the ones people follow. Policies that nobody has read are recorded as gaps, not as comfort.
We will not invent a risk score for you on this page, and we will not tell you that a tool, a firewall or a policy template is enough. The analysis is a conversation with the people who run the organisation. Consulting to close the gaps is quoted from what we find.
What ready means before a certification body arrives
NAM QMS does not issue ISO certificates and is not a certification body. An independent accredited certification body plans the audit and issues the certificate if it decides the system meets the standard. Readiness for ISO 27001 means the scope is written down, leadership has assigned responsibility, the risk assessment and the statement of applicability match the controls you operate, internal audits have tested those controls, and management review has seen incidents, audit results and changes in risk. Evidence is records of what you do, not a slide deck produced for the visit.
ISO 27001 does not certify a software product, a data centre you do not operate, or a promise that a breach can never happen. It certifies that the organisation's system for managing information-security risk meets the standard, and only the certification body makes that decision. Privacy extensions are a separate conversation; see the ISO 27701 consulting page if personal-data governance is the actual request.
Where this sits among the other Uganda guides
Quality, environment and safety systems do not replace an ISMS. If a tender asks for several standards, read ISO 9001 and ISO 45001 as their own scopes and keep information security defined on its own. Medical-device organisations that also hold patient or device data may need both this system and ISO 13485. They are not interchangeable.
The ISO certification in Uganda hub compares all five. Implementation services we already offer are on the ISO 27001 consulting page.
Questions organisations ask
Does NAM QMS issue ISO 27001 certificates?
No. NAM QMS trains teams and prepares the information security management system. An independent accredited certification body performs the audit and issues the certificate.
Is ISO 27001 a certificate for our software or our website?
No. The certificate, when a certification body issues one, covers the organisation's ISMS within the agreed scope. It is not a product test report and it is not a promise that an incident is impossible.
Who should be trained?
The people who will operate and audit the ISMS: information-security and IT leads, risk and compliance officers, and the managers who approve access and suppliers. We train organisational teams. This is not an individual career page.
Where do we see the course price?
On the ISO 27001:2022 Lead Auditor course page. That page is the source for the current fee. In-house ISMS training is quoted after the gap analysis, based on scope and team size.
What does the free gap analysis cover?
Scope, leadership and responsibilities, risk assessment and treatment, the controls you say you operate, internal audit and management review. You receive a practical picture of the gaps. You do not receive a certificate.
We already have ISO 9001. Do we still need a separate ISMS?
Yes, if the requirement is information security. A quality system does not assess information-security risk or select security controls. The two systems can share document control and management review, but the ISMS scope has to be its own.
Next step for your organisation
Book a free gap analysis if your organisation is working toward ISO 27001 certification in Uganda. We will identify who needs training and which parts of the ISMS are not yet ready for a certification body.
Book a free ISO gap analysis